Espilon Hunt
A closed-door hardware bug hunt where a validated patch earns as much as the discovery. Real products, two days on site, teams selected on application.
Espilon Learn
Hardware security training on IoT, OT and embedded devices. Courses, challenges, labs and device emulation.
What we find
A few of our published findings. See the full list on the advisories page.
CVE-2026-45328
Out-of-bounds write in the ESP-TEE secure service wrappers: a write primitive inside the part of the chip that's supposed to be trusted.
FreeRTOS-Plus-TCP & coreMQTT
Five CVEs in the network stack that ships on millions of devices: an RA out-of-bounds write, a DHCPv6 integer underflow, an MQTT v5 DoS and more.
CVE-2026-47773
Memory corruption in ArduinoBLE via a malformed ATT write request. Send the wrong bytes over Bluetooth, corrupt the parser's memory.
The framework
A fleet of ESP32 agents you reprogram on the fly to put byte-exact traffic on a target's real interfaces.

SimSift
Portable SIM card forensic tool on ESP32. Compatible with LilyGo T-Call and T-SIM7070G.
GitHub →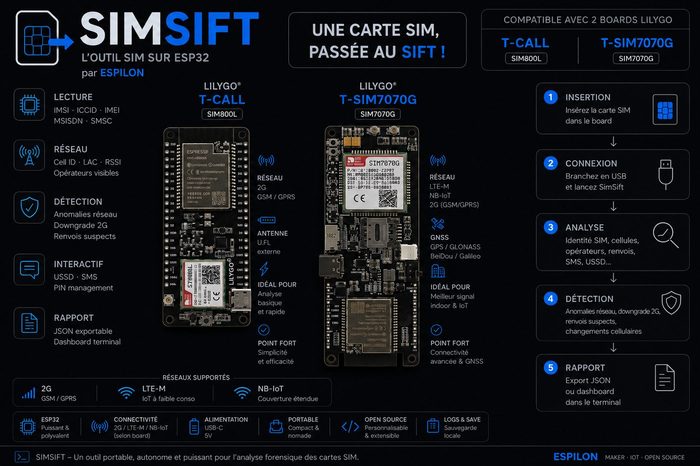
Espilon Monitor
Universal serial monitor for embedded devices. Watch multiple ports, detect crashes and events by regex pattern, fire Python hooks, stream structured JSON to your pipeline.
sudo apt install emon
brew install EspilonOrg/tap/emon
yay -S emon
Everything we ship
Framework, CTF, docs, blog and tools. All open, all linked below.
Platforms
Open-source tools
Resources
Come hang out
Write-ups, challenge support, hardware finds and IoT/OT talk. New challenges drop regularly.